Feith is FedRAMP Moderate Authorized → Read the release
Feith

One platform for the campus record.

The Feith Platform brings records and document management to colleges and universities, on the same architecture that manages federal agencies' permanent records. Every access writes to one append-only audit log.

14
Colleges, universities, and schools running Feith.
6
Compliance regimes configurable on one platform.
47 yrs
Building records technology since 1979.
45 days
The FERPA access window, tracked as a case from request to release.

One platform for the whole campus record, from the student file to sponsored research. Built and owned in Fort Washington, PA.

Six regimes. Twelve offices. One records officer holding the bag.

FERPA governs the student record. GLBA governs the aid file. NIST 800-171 covers anything CUI that arrives with a federal grant. State law and Title IX layer their own rules on top. And the records don't sit in one system.

  • FERPA the student record
  • GLBA Safeguards the financial-aid file
  • HIPAA campus health, where it applies
  • NIST 800-171 CUI from federal research
  • State public records open-records requests
  • Title IX investigation evidence

They live in Banner, PeopleSoft, Workday, M365, Google Workspace, file shares, and the paper folders some offices still keep, and the records officer is responsible for all of it. Feith takes responsibility for the records the moment they exist. Capture normalizes the metadata, the vault holds the authoritative copy, every access is logged, and retention runs against each office's schedule.

Students raising their hands in a university lecture hall
The lecture hall is where the record begins, and Feith governs it from the day it's created to the day it's disposed.

Every office on campus owns records. Feith covers every office.

Every office's records sit on the same vault and identity layer, with retention rules, access control, and logging configured to the regimes that office answers to.

Student records

Admissions · Financial Aid · Registrar / Transcripts · Bursar · Graduate School

The offices that own the official student record. Applications, transcripts, and award files come in from admissions and student systems through connectors or the Records API, and every release is tracked against the 45-day FERPA window.

Compliance FERPA · directory-information rules · GLBA Safeguards · Title IV evidence · NSLDS / COD retention.

Research & sponsored programs

Sponsored Programs · Research

Grant files, IRB and IACUC records, and the CUI that arrives with a federal research contract, all held in one campus vault.

Compliance NIST 800-171 · CMMC · ITAR · EAR · NIH and NSF retention.

People & faculty

HR / Faculty · Advancement / Alumni

Personnel files, tenure dossiers, search-committee records, and faculty contracts, plus gift records, donor files, and planned-giving documentation, separated from FERPA-protected records at the access layer where policy requires it.

Compliance EEOC · tenure schedule · CASE reporting standards · IRS substantiation.

Legal & public records

General Counsel / Public Records · Title IX / Conduct

Open-records requests, subpoena response, and e-discovery, alongside Title IX investigation files that need separated roles and a preserved evidence chain.

Compliance State public-records law · current Title IX requirements · Clery Act overlap · litigation hold.

Student health

Student Health (HIPAA-adjacent)

Counseling, health-services, vaccination, and accommodation records, held as FERPA treatment records, which the HIPAA Privacy Rule expressly excludes from protected health information, with HIPAA reaching the health center's non-student patients and ADA accommodation records kept separate.

Compliance FERPA treatment records · HIPAA for non-student patients · ADA accommodation rules.
FERPA is an architecture decision, built in from the start.

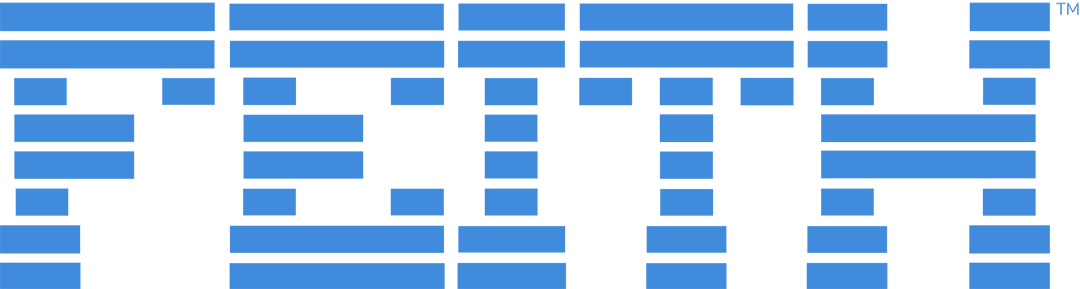
Feith treats FERPA as a structural requirement. Every access to a student record writes to an append-only log, the 45-day access window is a tracked workflow, and the school-official exception is logged with the determination that justified it.

  • Every read, write, and disclosure of a FERPA-covered record writes to the append-only audit log: user, role, action, timestamp, and record ID.
  • Role- and attribute-based access control reaches down to the record and field level, so each field of a student record follows the access rules your FERPA policy sets.
  • FERPA asks for reasonable methods to keep school officials inside their legitimate educational interest. Feith captures the reason at sign-in and logs every access, so the basis sits alongside the activity.
What one audit entry records
User · role
Who touched the record
Action
View · update · disclose
Session reason
Entered at sign-in, e.g. transcript processing
Stamp
Timestamp + record ID, immutable
Append-only · hash-verified · forwarded to your SIEM.
45-day access window: a tracked case

The clock starts on the request. The package returned to the requester is itself recorded.

The research office that holds federal contracts.

Federally-funded research carries federal records obligations: CUI markings, NIST 800-171 controls, ITAR and EAR export controls, CMMC posture for DoD work. Feith handles them on the same platform that handles your registrar's transcripts. The research office stops standing up parallel systems to satisfy compliance.

  1. 1
    Marked at capture
    The CUI marking is applied on intake and travels with the record.
  2. 2
    Enforced at access
    Checked at the user, record, and project level on every read; U.S.-person status verified.
  3. 3
    Audited to a control
    Every access is logged: your evidence, ready for a NIST 800-171 assessment.
  • CUI is marked at capture, propagated through the workflow, and enforced at access.
  • Logged access evidence supports your own NIST 800-171 assessment, so the record of who touched controlled research data is already assembled.
  • ITAR and EAR access restrictions are enforced at the user, record, and project level.
  • CMMC-relevant controls run on the single-tenant deployment: NIST 800-171 safeguards for CUI, enforced at access and evidenced in the log.
  • Sponsored-programs systems like Cayuse, Kuali, and InfoEd are integrated as capture sources during the project, so grant files flow into the same vault.

Public records and Title IX: the workflows under the most scrutiny.

State public-records requests arrive with a clock attached. Title IX files have to be retained, redacted, disclosed selectively, and held for years. Both run on the same vault, with the same exemption logic and redaction tooling as Feith's federal FOIA Workbench.

One identity. One audit log. Every record, every system.

Feith runs on the identity layer your campus already uses, and runs lifecycle and logging across records wherever they live, without forcing a migration.

One identity layer

SAML, Shibboleth, AD / LDAP, and MFA: the login your campus already uses, with role attributes derived from the SIS. Need-to-know access is enforced per record, per field, per workflow step.

One audit log

Append-only, hash-verified, anti-tamper, with Splunk / SIEM forwarding. The same logging federal agencies rely on holds your campus access log too.

One vault, every source system

Connectors capture from M365, Google Workspace, file shares, and the SIS, and a governed copy lands in the vault with its metadata intact. Your teams keep working in the tools they already use; retention, holds, and disposition run against the authoritative copy in the vault.

Move from the ECM you have today to the platform you need tomorrow.

Whatever ECM or homegrown stack your campus runs today, the migration happens in three phases, one at a time, so the path stops being all-or-nothing.

  1. 1

    Capture-only deployment

    Records flow into Feith from your existing systems while your incumbent ECM keeps running. Identity and logging consolidate first; the new vault carries everything that arrives after go-live without touching the legacy archive.

    No system retires in this phase.

  2. 2

    Department-by-department cutover

    Pick the office with the most pain. Sponsored Programs and Financial Aid are common first choices. Move that office's workflow, then repeat on a schedule the campus controls. Each cutover is independent.

    Sequenced to your priorities, one department at a time.

  3. 3

    Sunset, optional

    Some campuses retire the incumbent ECM once active workflows have moved; others keep it as a read-only archive. Either way, the Feith vault holds the authoritative copy of anything still in flight.

    When the campus is ready. The decision is reversible.

Forty-seven years of federal records work, now in your registrar's office.

The vault, identity layer, logging, and lifecycle services under the platform are the same components that hold federal agencies' permanent records, configured here to FERPA, GLBA, and your institution's retention schedules.

Bring the records architecture to your campus.

Book a walkthrough